Anasayfa Company Policies

Company Policies

SUSTAINABILITY POLICY

We take justifiable pride in having contributed to our country’s development for over half a century, and we shape our work around the slogan “Development and Beyond.” On our sustainability journey, which we have embarked upon with the aim of always doing better, we have defined our sustainability approach as “The Impact of Development.”

We view sustainability as an integral part of our corporate approach, and we accept and commit to implementing—and ensuring the implementation of—all our priorities and principles defined within the framework of sustainability, aiming for continuous improvement with the participation of our Group Companies and employees.

  • Through our Sustainability Policy, we embrace the principles outlined in the general framework below:
  • To be a steadfast supporter of the United Nations Sustainable Development Goals by conducting all our activities in alignment with these goals—particularly gender equality, decent work and economic growth, industry, innovation, infrastructure, and climate action—
  • To adhere to the highest ethical standards in all sectors and regions where we operate, and to act in compliance with applicable local laws, relevant international standards, and corporate governance principles in those regions;
  • To engage in activities that increase the share of renewable energy sources in the total energy supply in order to contribute to the fight against climate change, To reduce our energy consumption through energy efficiency measures; to measure our greenhouse gas emissions across all areas of our operations; to set reduction targets and implement projects accordingly; and to play an active role in our country’s green transition,
  • To continuously monitor and improve our processes to reduce our ecological footprint throughout our value chain, protect the environment and biodiversity, and contribute to the circular economy, To take all necessary measures in accordance with the highest health and safety standards to ensure a workplace with decent working conditions,
  • To prevent discrimination in all our processes and create employment opportunities for women, young people, and disadvantaged groups,
  • To offer our employees equal opportunities in all areas and to conduct hiring, career development, and promotion processes transparently and fairly,
  • To maintain the highest levels of employee satisfaction, regularly evaluate their feedback and suggestions, and implement necessary improvement initiatives,
  • To ensure customer satisfaction—one of our top priorities—by continuously improving the quality of our products and services and undertaking improvement initiatives,
  • In collaboration with the IC İbrahim Çeçen Foundation, as part of our corporate social responsibility projects, to support society and our stakeholders—particularly in the areas of education, health, sports, and the arts; and by establishing partnerships with various institutions and organizations in the regions where we operate, to conduct training and development activities aimed at raising local community awareness and enhancing their capabilities in the area of sustainability,
  • To support the development of our suppliers in this area by adopting sustainable supply chain practices in our procurement processes,
  • To regularly review our sustainability activities and processes; to set goals and objectives in light of identified risks and opportunities; and to regularly communicate our sustainability performance with all our stakeholders in accordance with the principles of transparency and accountability under international standards.

Purpose of the Policy
This policy aims to outline IC Holding and its Group Companies’ approach to and commitments regarding sustainability.

Scope of the Policy
This policy covers all our stakeholders, including our employees, subcontractors, suppliers, visitors, and the local community.

Implementation of the Policy and Relevant Legislation
This policy
has been developed by translating the rules established by applicable laws and international standards into concrete practices within the framework of our Company’s operations. In the event of any inconsistency between applicable laws and regulations and international standards and this policy, IC Holding acknowledges that the applicable laws and regulations shall prevail.

Effective Date of the Policy
It is reviewed periodically and updated as necessary. The Corporate Governance and Sustainability Directorate is responsible for updating this policy.

OUR OCCUPATIONAL HEALTH, SAFETY, AND ENVIRONMENTAL POLICY

At IC İÇTAŞ Construction, we are committed to ensuring the health, safety, and well-being of our employees, contractors, visitors, and the communities in which we operate. This Health, Safety, and Environment (HSE) Policy summarizes our commitment to maintaining the highest safety standards throughout our construction activities, preventing accidents, and protecting the environment.

Responsibilities: All employees, contractors, and visitors are required to comply with this HSE Policy. Management will provide the necessary resources, training, and support to ensure its successful implementation.

Compliance with Laws and Regulations: IC İÇTAŞ Construction will comply with all applicable health, safety, and environmental laws, regulations, and industry standards. Our practices will be continuously monitored and updated to meet or exceed these requirements. Our HSE performance will be regularly monitored and evaluated through established targets and performance indicators.

Risk Management: Potential health, safety, and environmental risks, hazards, and opportunities related to our construction activities will be identified and assessed. Risk assessments will be conducted regularly, and appropriate control measures will be implemented to eliminate or minimize hazards and risks.

Training and Competency: We will ensure that all employees and contractors have the necessary training and competency to perform their duties safely. Training programs will be regularly reviewed and updated to reflect best practices and changes in technology.

Safe Work Practices: Safe work practices are essential for preventing accidents. IC İÇTAŞ Construction will establish and communicate clear instructions regarding safe work practices at construction sites. Open communication regarding the reporting of safety concerns and unsafe conditions will be encouraged. The protection of employees’ physical and psychological health and the promotion of their well-being will be supported.

Emergency Preparedness: IC İÇTAŞ Construction will develop and maintain emergency response plans for various potential scenarios. Employees and contractors will receive training on emergency procedures and conduct periodic drills.

Environmental Protection: We are committed to minimizing our environmental impact by adopting sustainable practices, reducing waste, and using resources responsibly. We will comply with environmental regulations and make every effort to prevent pollution during construction activities.

Sustainability and Climate Change: We will adhere to national and international emissions targets; support energy efficiency to contribute to a low-carbon economy—one of the cornerstones of sustainable development—and regularly monitor our direct and indirect greenhouse gas emissions. Ensuring that these efforts are sustainable and traceable is our management commitment. We will support the efficient use of natural resources and keep water and energy consumption to a minimum. We will support the protection of biodiversity and the monitoring of impacts on ecosystems. All our activities will be conducted in accordance with the principles of sustainable development.

Incident Reporting and Investigation: All incidents, accidents, and near-misses will be reported immediately to management. IC İÇTAŞ Construction will conduct comprehensive investigations to determine the root causes of incidents and take corrective actions to prevent their recurrence.

Continuous Improvement: Our OSH Policy and practices will be regularly reviewed and updated to ensure their effectiveness and compliance. Feedback from employees, contractors, and stakeholders will be taken into account in the improvement process and evaluated using digital solutions.

Communication and Awareness: IC İÇTAŞ Construction will communicate this OHS Policy to all employees, contractors, and stakeholders to ensure they understand their roles and responsibilities in maintaining a safe and environmentally responsible workplace.

Subcontractors and Suppliers: We will collaborate with subcontractors and suppliers who share our commitment to health, safety, and environmental protection. Subcontractors will be expected to comply with our HSE standards and procedures. We will encourage our suppliers and business partners to operate in accordance with our OSH standards and monitor their performance.

Employee Engagement: We will conduct our operations transparently, addressing our employees’ concerns and contributing positively to their well-being.
Social Impact: Any potential negative impacts on the social environment will be prevented by establishing effective relationships with local communities.

İbrahim DÖNMEZ, General Manager
August 6, 2026

OUR QUALITY POLICY

As IC İÇTAŞ Construction, in line with our organization’s purpose and context, and in a manner that supports our strategic direction, we strive to be an organization that consistently meets or exceeds customer expectations, implements the requirements of the ISO 9001 quality management system, and delivers exceptional construction projects. This quality policy provides a framework for establishing and reviewing our quality objectives. By focusing on the following core principles, we aim to enhance our reputation as a reliable and preferred construction partner:

Customer Satisfaction: Our primary focus is on understanding and meeting our customers’ needs and expectations. We are committed to building long-term relationships with our customers based on transparency, integrity, and high-quality deliverables.

Quality Management System: We have established and maintain a robust Quality Management System (QMS) based on ISO 9001 standards. Our QMS provides a framework for continuous improvement, risk-based thinking, and compliance with applicable legal and regulatory requirements. We are committed to fully complying with all applicable legal, regulatory, and contractual requirements and to continuously improving the effectiveness of our quality management system.

Continuous Improvement: We are committed to monitoring, measuring, and analyzing our performance using key performance indicators (KPIs) that we continuously define to identify areas for improvement. Through data-driven decisions, we enhance our processes and services to achieve greater effectiveness and efficiency.

Supplier Collaboration: We are committed to working closely with our suppliers, subcontractors, and partners to ensure that the materials and services we receive meet the highest quality standards. By building strong relationships, we create a unified approach to ensuring quality throughout our projects.

Competent Workforce: Our success lies in the competence, expertise, and dedication of our workforce. We are committed to investing in their training, development, and certification to ensure they are equipped with the knowledge and skills necessary to deliver high-quality construction services.

Process Excellence: We are committed to continuously evaluating and improving our construction processes by monitoring KPIs to increase efficiency, reduce waste, and deliver projects on time and within budget. By focusing on process excellence, we deliver consistent and reliable results.

Health, Safety, and Environment: The well-being of our employees, subcontractors, and the environment is of the utmost importance. We prioritize health and safety measures in all our construction activities and are committed to minimizing our environmental impact. We comply with national and international regulatory requirements and are committed to operating in accordance with best practice standards.

Compliance and Accountability: We are committed to strictly adhering to QMS requirements and all applicable laws and regulations. Every employee is responsible for upholding the principles of our quality policy and the QMS.

Business Continuity: We are committed to assessing our risks and taking necessary measures to ensure we can continuously provide high-quality service to our customers, protect our company’s reputation, fulfill our legal obligations, and meet customer needs—even under the most adverse conditions.

Sustainability: We are committed to conducting all our operations in alignment with the United Nations Sustainable Development Goals, particularly Decent Work and Economic Growth, Industry, Innovation, Infrastructure, and Climate Action.

Making a Difference: To ensure continuity of service, we will continuously grow, invest in our growth process, generate resources for investment, and leverage technology. Recognizing that human resources are the most important factor in making all of this possible, we are committed to managing change through activities aimed at increasing our employees’ job satisfaction and highlighting their creativity and talents.

This quality policy is maintained as documented information; it is open to all employees, stakeholders, and relevant parties. It is communicated to our employees at our headquarters and construction sites; its understanding and implementation are ensured. We regularly review its suitability and effectiveness to ensure it remains aligned with our strategic objectives. This review is conducted at least once a year during Management Review meetings.

İbrahim Dönmez

General Manager

August 1, 2026

HUMAN RIGHTS POLICY

We place great importance on upholding human rights in all our activities, which we carry out with a focus on sustainable development. We embrace an approach that respects human rights for all our stakeholders—particularly our employees—and aim to promote the observance of human rights in society. In this context, we aim to provide a work environment that respects human rights and is equitable, inclusive, and fair for our employees. We offer equal opportunities to all our employees regardless of race, language, age, gender, religion, ethnic origin, or any other personal characteristic.

Through our Human Rights Policy, we embrace the principles outlined below as a general framework:

  • Acting with the awareness that people are our most important asset,
  • To act in accordance with applicable national and international laws and standards regarding working conditions across all sectors, both domestically and internationally,
  • To take the necessary measures to provide employees with a healthy and safe work environment while aiming to uphold human rights and provide a decent work environment,
  • To act in accordance with relevant local legislation and the international agreements to which Turkey is a party regarding forced labor and child labor,
  • To respect diversity by mutually accepting our differences,
  • To provide our employees with fair and appropriate compensation and benefits,
  • To create productive work and employment conditions that allow our employees to contribute their knowledge, expertise, skills, and experience in line with our company’s objectives, while respecting their contributions,
  • To prioritize the development of our employees at all levels and to continuously “invest in people” within the framework of the “continuous education and development” approach and in line with the company’s goals and strategies,
  • To treat our employees equally in all employment-related matters—including hiring, promotions, compensation, benefits, and training—as well as in all other processes, regardless of race, language, religion, religious beliefs, denomination, ethnic origin, age, position, gender, gender identity, sexual orientation, skin color, physical characteristics, country of birth, marital status, pregnancy, dependents, disability, social class, union membership, or political views; and to impose the necessary sanctions on those who engage in discrimination;
  • To follow a transparent and open management policy to ensure reliable and effective interaction.
  • To adopt a zero-tolerance policy regarding all forms of verbal, physical, psychological, sexual, and/or emotional harassment, and to provide a supportive environment where employees can exercise their right to freedom of expression to report such incidents when they occur;
  • Ensuring that our subcontractors and suppliers act in accordance with human rights standards and taking the necessary steps whenever any violation of human rights is detected,
  • To respect the rights of the communities in the regions where we operate, to strive to minimize negative impacts on their lives, to build long-term relationships by supporting stakeholder participation, and to take into account the expectations of all our stakeholders.

Purpose of the Policy

The purpose of this policy is to establish a framework for compliance with all relevant standards within the context of a decent work approach—primarily for our employees and all relevant stakeholders—to act in accordance with national and international laws and standards, and to continuously improve our efforts in this area.

Scope of the Policy

This policy covers our employees, subcontractors, suppliers, and local communities in the regions where we operate.

Implementation of the Policy and Relevant Legislation

This policy has been established by concretizing and codifying the rules set forth in current legislation within the framework of IC Holding’s practices. In this context, all relevant regulations—including, first and foremost, the Law on the Turkish Human Rights and Equality Agency, the Law on the Human Rights Investigation Commission, the Occupational Health and Safety Law, and the United Nations Convention on Human Rights—will take precedence. In the event of any inconsistency between the applicable legislation and this policy, IC Holding acknowledges that the applicable legislation shall prevail.

Effective Date of the Policy

This policy is reviewed periodically and updated as necessary. The Corporate Governance and Sustainability Directorate is responsible for updating this policy. The policy entered into effect on October 24, 2022, upon approval by the Board of Directors.

GENDER EQUALITY POLICY

We believe that gender equality is a key element of sustainable development, and we are committed to creating a workplace free of discrimination within our workforce. To this end, we make every effort to develop gender-neutral approaches in areas such as hiring processes, career development, promotions, work-life balance, compensation, and benefits.

Through our Gender Equality Policy, we embrace the principles outlined below as a general framework:

  • Promoting equal opportunity, diversity, and inclusion,
  • To take gender equality issues into account in planning, data collection, strategy development, and budget preparation processes for our activities,
  • Raising awareness about gender equality and inclusion in the workplace,
  • To improve our organizational culture through gender equality practices and activities by collecting feedback from within the organization via suggestion and complaint mechanisms,
  • To carry out initiatives aimed at preventing discrimination and harassment,
  • To adopt a zero-tolerance approach toward all forms of harassment (verbal, physical, sexual, psychological, and/or emotional), to establish a reporting mechanism for harassment cases, and to ensure that such cases are resolved through objective evaluation and appropriate sanctions,
  • To ensure that every employee has equal access to training and promotion opportunities,
  • To establish and continuously improve appropriate mechanisms to ensure that the gender equality perspective is reflected in hiring processes in a fair and transparent manner,
  • To ensure that the principle of gender equality is embraced at all levels of the organization through training, awareness campaigns, and social responsibility projects,
  • To develop supportive processes to help employees who are parents achieve a work-life balance,
  • To develop approaches that ensure all stakeholders act in accordance with IC Holding standards in the area of gender equality, To ensure that our suppliers, in particular, are made aware of how they can contribute to gender equality within our sphere of influence and to develop joint projects,
  • To play an active role in efforts toward gender equality in Turkey and around the world, we will establish collaborations and partnerships with various organizations—including national and international public institutions and organizations—and support projects in this field

Purpose of the Policy

The purpose of this policy is to establish a framework for creating a fair, unbiased work environment within the organization where no discrimination based on gender occurs among employees.

Scope of the Policy

This policy covers our employees, subcontractors, suppliers, and local communities in the regions where we operate.

Implementation of the Policy and Relevant Legislation

This policy commits to complying with and implementing applicable laws, regulations, and principles within the borders of Turkey. If the region in question falls outside the borders of Turkey, compliance with the applicable legislation of that country shall be ensured; in such cases, the more restrictive of the policy or the applicable legislation shall prevail. In the event of any inconsistency between the applicable legislation and this policy, IC Holding acknowledges that the applicable legislation shall prevail.

Effective Date of the Policy

The policy is reviewed periodically and updated as necessary. The Corporate Governance and Sustainability Directorate is responsible for updating the policy. The policy entered into effect on October 24, 2022, upon approval by the Board of Directors.

CORPORATE SOCIAL RESPONSIBILITY POLICY

In all our activities, we take an active role in the development of our country, the advancement of society, and the protection and support of the environment, while investing in the future. In our social responsibility initiatives, we focus on the İbrahim Çeçen Foundation—the leading organization at the forefront of our efforts— and in this regard, we take on a proactive and collaborative role to create added value for society and all our stakeholders through our impactful projects in various areas such as education, the arts, sports, the environment, and cultural development. In all our projects, we prioritize the local needs of the regions where we operate.

Through our Corporate Social Responsibility Policy, we embrace the principles outlined below as a general framework:

  • By recognizing the İbrahim Çeçen Foundation as our most important corporate social responsibility project, we commit to providing our stakeholders with timely, accurate, and complete information regarding our strategies, investments, and risks,
  • By fostering good relations with the local communities and people in the regions affected by our activities, we develop sustainable projects—from education to sports, and from the environment to the arts—that address social, societal, and environmental impacts with a sense of responsibility, and whose effects are measurable,
  • To actively participate in national and international reference forums and organizations that support behaviors and commitments related to corporate social responsibility,
  • To support social projects aimed at ensuring that disadvantaged groups—such as women, children, youth, and people with disabilities—are raised in a healthy, educated, and culturally enriched environment,
  • To develop social responsibility projects aimed at protecting and enhancing the ecosystem and cultural heritage within our areas of operation,
  • To develop quality education and learning opportunities for young people and future generations and to support projects in this regard,
  • To create social responsibility projects that support innovative ideas in collaboration with public institutions and organizations such as Ağrı İbrahim Çeçen University and other universities,
  • To develop approaches that ensure both our internal and external stakeholders act in accordance with IC Holding standards in the area of social responsibility, and to support them in volunteering for appropriate social and community activities in line with a sense of social responsibility,
  • To establish transparent mechanisms to address the concerns, suggestions, and/or complaints of all stakeholders regarding our projects, and to ensure that complaint channels through which they can submit feedback are fully functional.

Purpose of the Policy

The purpose of this policy is to contribute to the development of a sustainable awareness by embedding our corporate social responsibility philosophy into our corporate culture and to establish a policy for the continuous improvement of our efforts in this area.

Scope of the Policy

This policy covers our employees, subcontractors, suppliers, and local communities in the regions where we operate.

Implementation of the Policy and Relevant Legislation

This policy commits to complying with and enforcing the laws, regulations, and principles in effect within the borders of Turkey. In the event that the region in question falls outside the borders of Turkey, compliance with the applicable legislation of that country shall be observed; in such cases, whichever is more restrictive—the policy or the applicable legislation—shall prevail. In the event of any inconsistency between the applicable legislation and this policy, IC Holding acknowledges that the applicable legislation shall prevail.

Effective Date of the Policy

The policy is reviewed periodically and updated as necessary. The Corporate Governance and Sustainability Directorate is responsible for updating this policy. The policy entered into effect on October 24, 2022, following approval by the Board of Directors.

STAKEHOLDER ENGAGEMENT POLICY

We ensure that all internal and external stakeholders affected by—or potentially affected by—our operations are accurately informed about our activities, and we place great importance on enabling relevant stakeholders to contribute through consultation or participation in decisions that will affect them. We view our stakeholders’ opinions as a vital feedback mechanism that we actively use to improve our sustainability performance, and we ensure they contribute to our continuous improvement.

  • Through our Stakeholder Engagement Policy, we embrace the principles outlined below as a general framework: To act with an awareness of our responsibilities toward both our internal stakeholders—our employees—and all external stakeholders with whom we interact during the course of our operations,
  • To adopt an approach based on transparency, integrity, and loyalty in order to build stable relationships that foster trust with all our stakeholders,
  • To create a fair and efficient system aimed at identifying stakeholders who possess strong competencies and integrity, as well as a well-developed awareness of sustainability,
  • To provide clear, easily accessible, and constructive communication that is easily understood by our stakeholders and tailored to the needs of target groups,
  • To provide information through consultation activities prior to decision-making and to act in a manner that takes our stakeholders’ expectations into account,
  • To meet periodically with our stakeholders to organize events, seminars, and social activities, • To establish a two-way communication system that provides both parties with the opportunity to exchange views and information, listen, and hear concerns,
  • To respect local traditions, languages, and decision-making processes, and to ensure that all viewpoints are represented, including those based on religion, denomination, race, gender, political opinion, age, physical disability, and sensitive and/or minority groups,
  • To provide feedback at every stage by creating open and accessible mechanisms to respond to our stakeholders’ concerns, suggestions, and/or complaints,
  • Establishing a feedback system that enables us to receive opinions and complaints from our stakeholders on issues such as environmental and social performance and sustainability,
  • To set improvement targets for issues where satisfaction rates are low and dissatisfaction rates are high, and to track progress toward these targets,
  • Support stakeholders and programs that contribute to sustainable development and create shared value,
  • Identify areas for continuous improvement by comparing our stakeholder engagement performance with best practices,
  • To collaborate with our stakeholders to identify emerging trends and develop solutions for potential future problems,
  • To fulfill our social and environmental responsibilities toward the communities in the regions where we operate through harmonious collaboration with all our stakeholders.

Purpose of the Policy

This policy aims to understand our stakeholders and their needs, provide sufficient opportunities for them to express their views and ideas at all stages of relevant activities, establish a positive and trust-based working relationship with our stakeholders, and continuously improve our efforts in this area.

Scope of the Policy

This policy covers our employees, business partners, customers, investors, lenders, suppliers, subcontractors, regulatory authorities, civil society organizations, relevant international organizations, universities, and local and national government agencies.

Implementation of the Policy and Relevant Legislation

The Policy commits to complying with and implementing the laws, regulations, and principles in effect within the borders of Turkey. If the region in question falls outside the borders of Turkey, compliance with the applicable laws of that country shall be ensured; in such cases, the more restrictive of the Policy or the applicable laws shall prevail. In the event of any inconsistency between the applicable legislation and this policy, IC Holding acknowledges that the applicable legislation shall prevail.

Effective Date of the Policy

The Policy is reviewed periodically and updated as deemed necessary. The Corporate Governance and Sustainability Directorate is responsible for updating this policy. The policy entered into force on October 24, 2022, upon approval by the Board of Directors.

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 1/10


TABLE OF CONTENTS
  1. PURPOSE
  2. SCOPE
  3. DEFINITIONS
  4. RESPONSIBILITIES
  5. INTEGRATED MANAGEMENT SYSTEM OBJECTIVES
  6. RISK MANAGEMENT FRAMEWORK
  7. GENERAL PRINCIPLES OF THE INTEGRATED MANAGEMENT SYSTEM
  8. POLICY VIOLATIONS AND SANCTIONS
  9. MANAGEMENT REVIEW
  10. UPDATING AND REVIEWING THE INTEGRATED MANAGEMENT SYSTEM POLICY DOCUMENT


PREPARED BY APPROVED BY
IMMS MANAGEMENT REPRESENTATIVE CEO

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 2/10


1. Purpose

The purpose of this policy is to prevent violations of legal, statutory, regulatory, or contractual obligations, as well as any security requirements, within the organization’s physical framework, to prevent violations of legal, regulatory, or contractual obligations and all security requirements under the ISO/IEC 27001 standards, and to communicate these objectives to all employees and relevant parties.

2. Scope

The protection of electronic information assets generated from commercial activities conducted within the organization and from information systems, accounting, reporting, operations, customer relations, complaints, risk management, and internal management activities; the processing, storage, and protection of personal data held within the company in accordance with the law; and the information security processes used to ensure that the confidentiality and integrity of such data are not compromised.

3. Definitions

ISMS: Information Security Management System.

Information Security Management System Manual: An informational booklet prepared to educate staff about information security and to define objectives.

Inventory: All types of information assets that are important to the company.

Know-How: The ability to perform a specific task.


PREPARED BY APPROVED BY
ISMS MANAGEMENT REPRESENTATIVE CEO

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 3/10

Information Security: Information, like all other corporate and commercial assets, is a valuable asset for a business and must therefore be properly protected. Within the company, know-how, processes, formulas, techniques and methods, customer records, marketing and sales information, personnel information, and commercial, industrial, and technological information and secrets are considered CONFIDENTIAL INFORMATION.

Confidentiality: The restriction of access to the content of information so that it is viewable only by those authorized to access the information or data. (Example: Even if an encrypted email is intercepted, unauthorized individuals can be prevented from reading it through Registered Electronic Mail – KEP)

Integrity: The ability to detect unauthorized or accidental modification, deletion, or addition/removal of information, and ensuring that such detection is guaranteed. (Example: Storing data in a database along with its hash values—electronic signature—mobile signature)

Availability: The asset must be ready for use whenever needed. In other words, systems must remain continuously operational, and the information within them must not be lost and must remain continuously accessible.

Information Assets: These are assets owned by the company that are essential for conducting its operations without disruption. Within the scope of the processes covered by this policy, information assets include the following:

  • Any type of information and data presented in paper, electronic, visual, or audio formats,
  • Any software and hardware used to access or modify information,


PREPARED BY APPROVED BY
ISMS MANAGEMENT REPRESENTATIVE CEO

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 4/10
  • Networks that facilitate the transfer of information,
  • Facilities and private areas,
  • Departments, units, teams, and employees,
  • Solution partners,
  • Services, products, or offerings provided by third parties.

4. RESPONSIBILITIES

Responsibilities and authorities are defined in job descriptions based on the qualifications and competencies required for each role. The Integrated Management System Management Representative is responsible for maintaining and developing activities related to the Integrated Management System.

The Integrated Management System Management Representative is appointed by the General Manager.

4.1. Management Responsibility

  • Company Management commits to complying with the defined, implemented, and active Integrated Management System; to allocating the necessary resources to ensure the system operates efficiently; and to ensuring that the system is understood by all employees.


PREPARED BY APPROVED BY
BGYS MANAGEMENT REPRESENTATIVE CEO

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 5/10
  • The Management Representative is appointed via an appointment letter during the establishment of the BGYS. When necessary, the Board of Directors revises the document and reappoints the representative.
  • Managers at the management level assist by delegating responsibility for safety to lower-level staff and by setting an example. The approach established and implemented by the Board of Directors must extend all the way down to the company’s lowest-level employees. Therefore, all managers support their employees—both verbally and in writing—to ensure they comply with safety instructions and participate in safety-related activities.
  • The Board of Directors establishes the budget required for comprehensive work within the integrated management system.

4.2. Responsibilities and Duties of the BGYS Management Representative

  • Work in accordance with the BGYS Policy and Objectives
  • Organize the creation, implementation, and maintenance of the necessary documentation for the Integrated Management System.
  • Reporting to top management whenever there is a need regarding the performance and improvement of the Integrated Management System.
  • Ensure that procedures are prepared, review them for compliance with the BGYS, and approve them,


PREPARED BY APPROVED BY
BGYS MANAGEMENT REPRESENTATIVE CEO

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 6/10


  • To raise awareness of the BGYS within the company by providing various training sessions at all levels,
  • Ensure that awareness of customer requirements is widespread throughout the organization;
  • To collaborate with external parties on matters related to the Integrated Management System.
  • Ensure that all departments operate in accordance with the information technology quality objectives and policies and establish coordination.
  • To prepare or review procedures, instructions, and forms and submit them to the Company Manager for approval.
  • Ensure that corrective actions are initiated, carried out, and monitored through the appropriate channels.
  • To plan and monitor internal audit activities to ensure that all functions within the scope of the Integrated Management System are audited at least once a year.
  • Include internal audit findings on the agenda of the Management Review Meeting.
  • Monitor the implementation of decisions made at the Management Review Meeting.
  • Manage and maintain control over the records of the Integrated Management System.
  • Comply with the general operating rules of the Information Technology department.


PREPARED BY APPROVED BY
BGYS MANAGEMENT REPRESENTATIVE CEO

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 7/10


4.3. Duties of the Information Technology Officer

  • Manage information technology operations
  • To conduct budget planning
  • Work in accordance with the BGYS Policy and Objectives
  • Monitor the implementation of decisions made at the Management Review Meeting.
  • To carry out the management and control of Integrated Management System records.
  • Act in accordance with the general operating rules of Information Technology.
  • Performing the duties assigned to them in policies, procedures, and instructions.

5. INTEGRATED MANAGEMENT SYSTEM OBJECTIVES

To protect all information assets within its critical systems; to operate in compliance with legislation, contracts, and international standards within the framework of the Integrated Management System; Manage risks within the Integrated Management System, implement corrective and improvement actions, and establish a sustainable system in line with the organization’s purpose. The objectives set by Management are monitored at specified intervals and reviewed during Management Review meetings.

PREPARED BY APPROVED BY
BGYS MANAGEMENT REPRESENTATIVE CEO

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 8/10


6. RISK MANAGEMENT FRAMEWORK

The company’s risk management framework covers the identification, assessment, and treatment of information security risks. The risk analysis, statement of applicability, and risk treatment plan define how information security risks are controlled. The ISMS Management Representative is responsible for the management and implementation of the risk treatment plan. All of these activities are detailed in the asset inventory and risk assessment procedure.

7. GENERAL PRINCIPLES OF THE INTEGRATED MANAGEMENT SYSTEM

7.1. Company employees and third parties are required to be familiar with this policy and the procedures it outlines, as well as the information security requirements and rules it establishes, and to conduct their work in accordance with these rules.

7.2. Unless otherwise specified, these rules and policies must be taken into account for the use of all information—whether stored and processed in printed or electronic form—and all information systems.

7.3. The Integrated Management System is structured and operated based on the TS ISO/IEC 27001 standard.

7.4. The implementation, operation, and improvement of the ISMS are carried out with the contribution of relevant parties. The ISMS Management Representative is responsible for updating ISMS documentation as needed.

7.5. The information systems and infrastructure provided by the company to employees or third parties, as well as all types of information, documents, and products generated using these systems, belong to the company unless otherwise required by law or contract.

7.6. Confidentiality agreements are entered into with employees, consultants, service providers (security, maintenance, catering, cleaning companies, etc.), suppliers, and interns.

PREPARED BY APPROVED BY
BGYS MANAGEMENT REPRESENTATIVE CEO

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 9/10

7.7. Information security controls to be applied during hiring, job reassignment, and termination processes are defined and implemented.

7.8. Training sessions designed to increase employees’ information security awareness and ensure their contribution to the system’s operation are regularly provided to current and new employees.

7.9. All actual or suspected information security breaches are reported; nonconformities causing breaches are identified, root causes are determined, and measures are taken to prevent recurrence.

7.10. An inventory of information assets is created in accordance with integrated management requirements, and ownership of the assets is assigned.

7.11. Corporate data is classified, and the security requirements and usage rules for each class of data are defined.

7.12. Physical security controls are implemented in accordance with the needs of assets stored in secure areas.

7.13. Necessary controls and policies are developed and implemented to protect the company’s information assets against physical threats they may face both inside and outside the organization.

7.14. Procedures and instructions related to capacity management, third-party relationships, backup, system acceptance, and other security processes are developed and implemented.

7.15. Audit log generation configurations for network devices, operating systems, servers, and applications are set in accordance with the security requirements of the relevant systems. Audit logs are protected against unauthorized access.

7.16. Access rights are assigned on a need-to-know basis. The most secure technologies and techniques available are used for access control.

7.17. Security requirements are defined during system procurement and development, and compliance with these requirements is verified during system acceptance or testing.

PREPARED BY APPROVED BY
ISMS MANAGEMENT REPRESENTATIVE CEO

IC Holding Logo

INFORMATION SECURITY POLICY

Document No. IC.YS.PLTK.04
Publication Date July 2, 2024
Revision No. 00
Revision Date –
Page No. 10/10


7.18. Continuity plans for critical infrastructure are prepared, maintained, and tested.

7.19. The necessary processes are designed to ensure compliance with laws, internal policies and procedures, and technical security standards; compliance is ensured through continuous and periodic monitoring and audit activities.

8. POLICY VIOLATIONS AND SANCTIONS

If non-compliance with the Integrated Management System Policy and Standards is detected, the sanctions specified in the Disciplinary Procedure are applied to the employees responsible for the violation.

9. MANAGEMENT REVIEW

Management review meetings are organized by the Integrated Management System Management Representative, with the participation of the Board of Directors and Department Heads. These meetings, during which the suitability and effectiveness of the Integrated Management System are evaluated, are held at least once a year.

10. UPDATE AND REVIEW OF THE INTEGRATED MANAGEMENT SYSTEM POLICY DOCUMENT

The IMS Management Representative is responsible for ensuring the continuity and review of the policy document. Policies and procedures must be reviewed at least once a year. In addition, they must be reviewed following any changes that affect the system structure or risk assessment, and if any changes are necessary, they must be approved by senior management and recorded as a new version. Each revision must be published in a manner accessible to all users.
COOKIE POLICY

This Cookie Policy applies to visitors to the website (“Website”) operated by IC İçtaş Construction Industry and Trade Joint Stock Company (“IC İçtaş”), located at Merkez Mahallesi, Silahşör Cad., Hilton Hotel Apt., No: 42/1, Şişli/Istanbul, and operating under Tax Identification Number (VKN) 4700005438, and the website consisting of this domain name and its subdomains (“Website”) has been prepared to ensure that the personal data of visitors processed through cookies is handled in accordance with the Constitution of the Republic of Turkey, international treaties on human rights to which our country is a party, and the Law No. 6698 on the Protection of Personal Data (“KVKK”), as well as other relevant legislation, and to ensure that data subjects whose personal data is processed can effectively exercise their rights. All personal data shared with IC İçtaş will be processed in a lawful manner, in a way that is relevant to and proportionate to the purposes of IC İçtaş’s activities and services.

Definitions

The terms “personal data,” “sensitive personal data,” and “data processing” used in this Cookie Policy are defined in accordance with the definitions set forth in the KVKK. The term “personal data” as defined in the KVKK refers to any information relating to an identified or identifiable natural person; the term “processing of personal data” refers to the collection, stored, retained, modified, reorganized, disclosed, transferred, acquired, made accessible, classified, or restricted from use.

Principles of Personal Data Processing

Pursuant to Article 4 of the Personal Data Protection Law (KVKK), personal data belonging to the data subject shall be processed by the data controller, IC İçtaş, in accordance with the following principles: in compliance with the law and the principles of good faith; accurate and, where necessary, up-to-date; for specific, explicit, and legitimate purposes; relevant, limited, and proportionate to the purpose for which they are processed; and in accordance with the rules governing retention for the period prescribed by applicable legislation or as necessary for the purpose of processing, by the data controller, IC İçtaş, within the scope of the purposes specified below.

What Is a Cookie?

A cookie is a small text file that may be used to access information about visitor activities on the Website, perform analyses, and collect data to ensure the Website functions properly. It is important to note that cookies do not collect information about files stored on visitors’ devices. If the visitor currently accepts cookies, the cookies placed on the visitor’s device may be used in accordance with this Cookie Policy, or if the visitor has previously visited the Website or consented to these cookies. While the use of cookies is not mandatory to use the Website, visitors may block and/or customize cookies through their browser. However, if cookies are blocked, visitors will not be able to use certain features of the Website. Furthermore, depending on browser settings, these cookies may not be automatically deleted; therefore, as detailed in the Cookie Policy, it is crucial for visitors to check their browser settings to determine where cookies are stored and how they can be deleted.

In addition to these, the Website also uses certain technologies for purposes similar to those of cookies. These include: pixel tags, which are transparent graphic images placed on a website to indicate that a page has been viewed; mobile device identifiers, such as IDFA and advertising ID, which are used to store information regarding a mobile device’s usage in third-party environments; segmentation/reporting products—programs and/or products that operate through pre-built code added to the Website or mobile devices via various methods and, through this code, report on, interpret, and store users’ activities on the Website or mobile devices.

Cookie Types and Purposes of Use

Essential Cookies: These cookies are necessary for the Website to function properly. The use of these cookies is mandatory to ensure the Website continues to function and can be maintained without issues. These cookies do not collect data for the purpose of marketing to visitors, remembering where a visitor is on the Internet, or tracking visitors. Since the data collected through these cookies must be used and protected on the Website, it is not possible to disable essential cookies.

Analytical Cookies: These cookies enable the identification of visitors, the counting of visitors for analytical purposes, and the determination of how visitors navigate the Website. These cookies help improve the Website’s functionality and make it easier for visitors to find what they are looking for.

Functional Cookies: These cookies are used to recognize visitors when they return to the Website. These cookies help personalize the Website for individual visitors and, as a result, remember their preferences.

Marketing Cookies: These cookies can be used to present content and campaigns relevant to the visitor and their interests, as well as to deliver targeted ads or limit the number of times an ad is displayed.

Comprehensive information about the cookies used on the Website and their purposes is provided in the table below;

Cookie Type Cookie Name Source Purpose Lifetime
Performance _ga Google Analytics This cookie is used by Google Analytics to evaluate the purpose of a visitor’s session, generate reports on website activity for website administrators, and improve the visitor experience. 540 Days
Analytics _gat Google Analytics Used by Google to limit the user’s request rate during times of high traffic on the website. 1 Minute
Analytics _gid Google Analytics Used by Google to store information about how visitors use the website. 1 Day
First-party, session cookie (required) ASP.NET_Sessionld ASP.NET Used to maintain the user’s connection to the server throughout their session. The user is associated with the same session for every page request. Without this cookie, the ASP.NET application cannot recognize the user throughout the session. For the duration of the browser session

Disabling and Deleting Cookies

Visitors can disable all or some cookies by enabling the relevant setting in their browser. However, if visitors disable all cookies—including those that are essential—using their browser settings, they will not be able to access all or part of the Website. It is important to note that disabling a cookie or a cookie category does not delete the cookie from the visitor’s device. This action must be performed separately through the visitor’s browser.

Visitors who wish to change their cookie settings should review the “Options” or “Preferences” section in their browser. For more information, it is highly recommended to review the “Help” section of various browsers, including Internet Explorer, Firefox, Chrome, Android, Safari, and iOS.

Transfer of Your Personal Data

IC İçtaş acts in accordance with the regulations set forth in the Personal Data Protection Law (KVKK) regarding the transfer of personal data. Subject to the exceptions set forth in the legislation or listed below, personal data and special-category personal data are not transferred by us to other natural or legal persons without the Data Subject’s explicit consent. In the exceptional cases provided for by the KVKK and other applicable laws, we exercise the utmost care to ensure that the transfer of personal data to authorized administrative or judicial bodies or private organizations is carried out in accordance with the forms and limitations stipulated by law.

Your personal data may be transferred:

To authorized public institutions and organizations, as well as private individuals legally authorized, for the purpose of fulfilling legal obligations;

To relevant judicial authorities, including attorneys, for the purpose of conducting or ensuring the follow-up of judicial proceedings; in accordance with the procedures and principles set forth in the relevant legislation and consistent with the conditions and purposes for the transfer of personal data specified in Articles 8 and 9 of the Personal Data Protection Law (KVKK).

Method and Legal Basis for the Collection of Personal Data/Sensitive Personal Data

Your personal data may be collected automatically when you access the Website. The legal grounds for the processing of your personal data by IC İçtaş are the exceptions to the requirement for explicit consent specified in Articles 5/2/a, 5/2/c, 5/2/ç, 5/2/e, and 5/2/f, as well as the exceptions to the requirement for explicit consent specified in Article 6/3. Your personal data is collected by IC İçtaş in accordance with all applicable laws and regulations based on the aforementioned legal grounds.

Data Subject’s Rights

The data subject may contact IC İçtaş, acting as the data controller, to: learn whether their personal data has been processed; if so, request information regarding such processing; learn the purpose of the processing of their personal data and whether it is being used in accordance with that purpose; to be informed about third parties to whom their personal data has been transferred, whether within or outside the country; to request the correction of their personal data if it has been processed incompletely or incorrectly; to request the erasure or destruction of their personal data within the framework of the conditions specified in Article 7 of the KVKK; to request that the actions taken pursuant to Articles 11/d and 11/e of the KVKK be notified to the third parties to whom their personal data has been transferred; to object to a decision made solely through the automated analysis of processed data that results in a negative outcome for the individual; the right to request compensation for damages incurred as a result of the unlawful processing of personal data.

In accordance with the Communiqué on the Procedures and Principles for Applications to the Data Controller, applications submitted by you must include your first name, last name, a signature if the application is in writing, or an electronic signature or mobile signature if submitted electronically, Turkish ID number (TCKN), the residence or business address used for service of process, the email address used for notification (if any), phone number, and information regarding the subject of the request. To exercise the rights specified above, the data subject is required to clearly and comprehensibly state the matter requested in the application—which must include an explanation of the relevant right—and to attach the necessary information and documents to the application.

The aforementioned applications may be submitted:

  • submitted in person, by hand, or in writing to IC İçtaş at “Merkez Mahallesi Silahşör Cad. Hilton Otel Apt. No: 42/1 Şişli/İstanbul,”
  • by sending a request through a notary public to IC İçtaş’s address at “Merkez Mahallesi Silahşör Cad. Hilton Otel Apt. No: 42/1 Şişli/İstanbul,”
  • or by sending them via Registered Electronic Mail (KEP) to the same address.

For a third party other than the data subject to submit a request, a notarized special power of attorney issued by the data subject in the name of the person making the request must be provided. Additionally, the request must include the requester’s identification and address information, and documents verifying the requester’s identity must be attached. Requests made by unauthorized third parties on behalf of others will not be considered. To exercise the rights specified above, the data subject must clearly and unambiguously state the specific matter being requested in the application, which must include an explanation of the right being exercised. Information and documents related to the request must be attached to the application.

Requests submitted to IC İçtaş in accordance with the proper procedure will be resolved within thirty days at the latest. If the resolution of your requests entails additional costs, IC İçtaş will charge the applicant a fee in accordance with the schedule determined by the Personal Data Protection Board (“Board”). If IC İçtaş responds to your application via a storage medium such as a CD or flash drive, a fee may be charged, provided that the amount does not exceed the cost of the storage medium. IC İçtaş may request the necessary information and documents from you to determine whether you are the actual owner of the personal data in question and may ask you questions regarding your request to clarify the matters specified therein.

IC İçtaş will notify you of its response to your request in writing or electronically. In accordance with Article 14 of the KVKK, if your request is rejected, if you deem the response provided by IC İçtaş insufficient, or if no response is provided within the prescribed timeframe; you may file a complaint with the Board within 30 (thirty) days from the date you receive IC İçtaş’s response—or, if no response is provided, from the expiration of the response period—and in any case, within 60 (sixty) days from the date of your request.

İÇTAŞ CONSTRUCTION, INDUSTRY, AND TRADE CORPORATION
PRIVACY NOTICE REGARDING THE PROCESSING OF YOUR PERSONAL DATA

As İçtaş Construction, Industry, and Trade Joint Stock Company (“the Company”), we place the utmost importance on ensuring the security of your personal data. In this context, in accordance with the Personal Data Protection Law No. 6698 (“PDPA”), during the processing of your personal data and its transfer to third parties, we take the necessary measures to ensure an appropriate level of security to prevent the unlawful processing of your personal data and unlawful access to it, and to ensure the protection of your personal data. For this reason, this document has been prepared to inform data subjects.

This document will be updated if the entire text or specific provisions organized by our company are revised.

1. THE DATA CONTROLLER:

As a company, we are the legal entity that determines the purposes and means of processing your personal data and is responsible for the establishment and management of the data processing system. Upon your explicit consent to the processing of your personal data—or, in cases where explicit consent is not required, following the information we provide—our Company will begin processing your personal data while ensuring data security. While processing your personal data, we may also have one or more data processors process your personal data on our behalf, provided that we ensure the necessary level of security by authorizing them to do so.

2. LEGAL BASIS FOR THE PROCESSING OF YOUR PERSONAL DATA, METHODS BY WHICH IT MAY BE COLLECTED, AND WHAT PERSONAL DATA WILL BE PROCESSED:

Your personal data will be processed by our Company in accordance with the provisions of applicable legislation to provide the services to be rendered and to improve the quality of these services; to carry out activities required by public authorities and/or deemed to be exceptions; to fulfill the Company’s operations; and for data storage, reporting, and to comply with information disclosure obligations. Additionally, to enable you to visit our Company, to protect security and legitimate interests related to your visit, to offer our Company’s products and services, to establish communication regarding the products and services you have received or will receive, and to provide services related to our Company’s areas of operation—such as product/service offers, modeling, reporting, scoring, and risk monitoring—as well as to enhance the quality of these services, carry out other activities, and comply with disclosure obligations—one or more, or all, of your personal data listed in Annex 1 may be processed.

For this purpose, we may share the personal data we process with our affiliates, business partners, suppliers, company officials, shareholders, group companies, and public institutions and private individuals authorized by law, both within Turkey and abroad.

3. SHARING OF YOUR PERSONAL DATA:

Your personal data may be collected verbally, in writing, or electronically—in accordance with the provisions of applicable legislation—through our Company, our affiliates, our business partners, and our employees, as well as via our website, social media channels, and any other means.

This information notice serves as an annex and an integral part of any contract you have signed with our Company and of your requests for the provision of services.

4. DISPOSAL OF YOUR PERSONAL DATA:

Our Company retains your processed personal data for the periods specified by law. However, in cases where the law does not specifically stipulate a retention period for your personal data, your personal data will be retained for as long as necessary to process such data in accordance with our Company’s practices and commercial customs, as required by the services we provide while processing that data, and thereafter, only for the periods deemed necessary in practice to serve as evidence in potential legal disputes. Upon the expiration of the specified periods, in accordance with Article 7 of the Personal Data Protection Law, your personal data in question will be deleted, destroyed, or anonymized on the first applicable date.

5. YOUR RIGHTS REGARDING THE PROCESSING OF YOUR PERSONAL DATA:

Under Article 11 of the Personal Data Protection Law, you may submit the following requests to our Company by contacting us:

  1. To learn whether your personal data has been processed and, if so, to request information regarding such processing,
  2. To learn the purpose of the processing of your personal data and whether it is being used in accordance with that purpose,
  3. To learn the third parties to whom your personal data has been transferred, whether within or outside the country,
  4. To request the correction of your personal data if it has been processed incompletely or incorrectly,
  5. To request the erasure, destruction, or anonymization of your personal data if the grounds for processing it under Article 7 of the Personal Data Protection Law no longer exist,
  6. To request that the actions taken pursuant to subparagraphs (d) and (e) be notified to the third parties to whom your personal data has been transferred,
  7. To object to a decision made solely through the automated processing of your personal data that adversely affects you,
  8. To request compensation for damages incurred as a result of the unlawful processing of your personal data.

You may exercise the rights listed above in accordance with the provisions of the Personal Data Protection Law, the Communiqué on the Procedures and Principles for Applications to the Data Controller published on March 10, 2018, and relevant current legislation by using the application form available at www.ictas.com.tr;

  1. by submitting a hand-signed petition in person at the address: Merkez Mahallesi, Silahşör Caddesi, Hilton Hotel, No. 42/1, Şişli/Istanbul, or by having it sent to this address via a notary public,
  2. Via Registered Electronic Mail to the address [email protected],
  3. By email to [email protected], including a secure electronic signature or mobile signature,

Applications may be submitted in the following ways:

Information regarding the specific application channels through which your applications can be submitted to us is provided below.

Application Method Address for Submission (in the event of an address change, the most recent address published in the Commercial Registry Gazette must be used) Information to Be Included in the Application
In-Person Application (The applicant must appear in person and submit the application with a valid form of identification) Merkez Neighborhood, Silahşör Street, Hilton Hotel, No. 42/1, Şişli/Istanbul The envelope must be marked “Request for Information Under the Law on the Protection of Personal Data.”
Service of Process via Notary Merkez Neighborhood, Silahşör Street, Hilton Hotel, No. 42/1, Şişli/Istanbul The envelope for the service of process must be marked “Request for Information Under the Law on the Protection of Personal Data.”
Via Registered Electronic Mail (KEP) [email protected] The subject line of the email must read “Request for Information Under the Personal Data Protection Law.”
Via email, including a secure electronic signature or mobile signature [email protected] The subject line of the email must read “Request for Information Under the Personal Data Protection Law.”

If a request is submitted by someone other than the data subject, a notarized special power of attorney issued by the data subject in the name of the person making the request must be provided.

Requests submitted to our Company in accordance with the proper procedures within this scope will be resolved within thirty days at the latest. If the resolution of your request entails additional costs, our Company will charge the applicant a fee in accordance with the tariff established by the Personal Data Protection Board (“Board”). If our Company responds to your request via a storage medium such as a CD or flash drive, a fee may be charged, provided that the amount does not exceed the cost of the storage medium.

Our Company may request the necessary information and documents from you to determine whether you are the actual owner of the personal data in question, and may ask you questions regarding your request to clarify the matters specified therein.

Our company may reject your request, providing an explanation of the grounds, in the following cases:

  • The processing of your personal data for purposes such as research, planning, and statistics, where such data has been anonymized through official statistical methods.
  • The processing of your personal data for artistic, historical, literary, or scientific purposes, or within the scope of freedom of expression, provided that such processing does not violate national defense, national security, public safety, public order, economic security, the privacy of private life, or personal rights, nor does it constitute a crime.
  • The processing of your personal data within the scope of preventive, protective, and intelligence activities carried out by public institutions and organizations authorized by law to ensure national defense, national security, public safety, public order, or economic security.
  • The processing of your personal data by judicial authorities or enforcement agencies in connection with investigations, prosecutions, trials, or enforcement proceedings.
  • The processing of your personal data when necessary to prevent the commission of a crime or for the purposes of a criminal investigation.
  • The processing of your personal data that you have made public.
  • The processing of your personal data is necessary for the performance of supervisory or regulatory duties, or for disciplinary investigations or prosecutions, by competent and authorized public institutions and organizations, as well as professional organizations with the status of public institutions, based on the authority granted by law.
  • The processing of your personal data is necessary to protect the State’s economic and financial interests regarding budgetary, tax, and financial matters.
  • There is a possibility that your request may infringe upon the rights and freedoms of others.
  • You have made requests that would require a disproportionate amount of effort on our part.
  • The information you have requested is publicly available.

Our Company will notify you of its response to your request in writing or electronically. In accordance with Article 14 of the Personal Data Protection Law, if your request is rejected, if you find the response provided by our Company insufficient, or if no response is provided within the prescribed timeframe; You may file a complaint with the Board within 30 (thirty) days from the date you receive our response—or, if we fail to respond, from the expiration of the response period—and in any case, within 60 (sixty) days from the date of your request.

APPENDIX 1: Categories of Personal Data
Identity Information Information clearly belonging to an identified or identifiable natural person; processed either partially or fully automatically, or non-automatically as part of a data recording system; such as all information contained in documents including Driver’s License, National ID Card, Residence Permit, Passport, Attorney’s ID, marriage certificates
Contact Information Information that clearly pertains to an identified or identifiable natural person; processed either partially or fully automatically, or non-automatically as part of a data recording system; such as phone number, address, and email address
Physical Premises Security Information Personal data clearly belonging to an identified or identifiable natural person and contained within a data recording system; personal data related to records and documents collected upon entry to a physical location and during the time spent within that location
Transaction security information Personal data clearly belonging to an identified or identifiable natural person and stored within the data recording system; your personal data processed for the purpose of ensuring compliance with technical, administrative, legal, and commercial obligations while conducting our business activities
Risk management information Personal data clearly belonging to an identified or identifiable natural person and contained within the data recording system; personal data processed through methods used in accordance with generally accepted legal, commercial practices, and the principle of good faith in these areas to enable us to manage our commercial, technical, and administrative risks
Financial information Personal data clearly attributable to an identified or identifiable natural person, processed either partially or fully automatically or non-automatically as part of a data recording system; personal data of subcontractors, supplier representatives, or employees relating to information, documents, and records reflecting the individual’s financial status in any form
CERTIFICATES
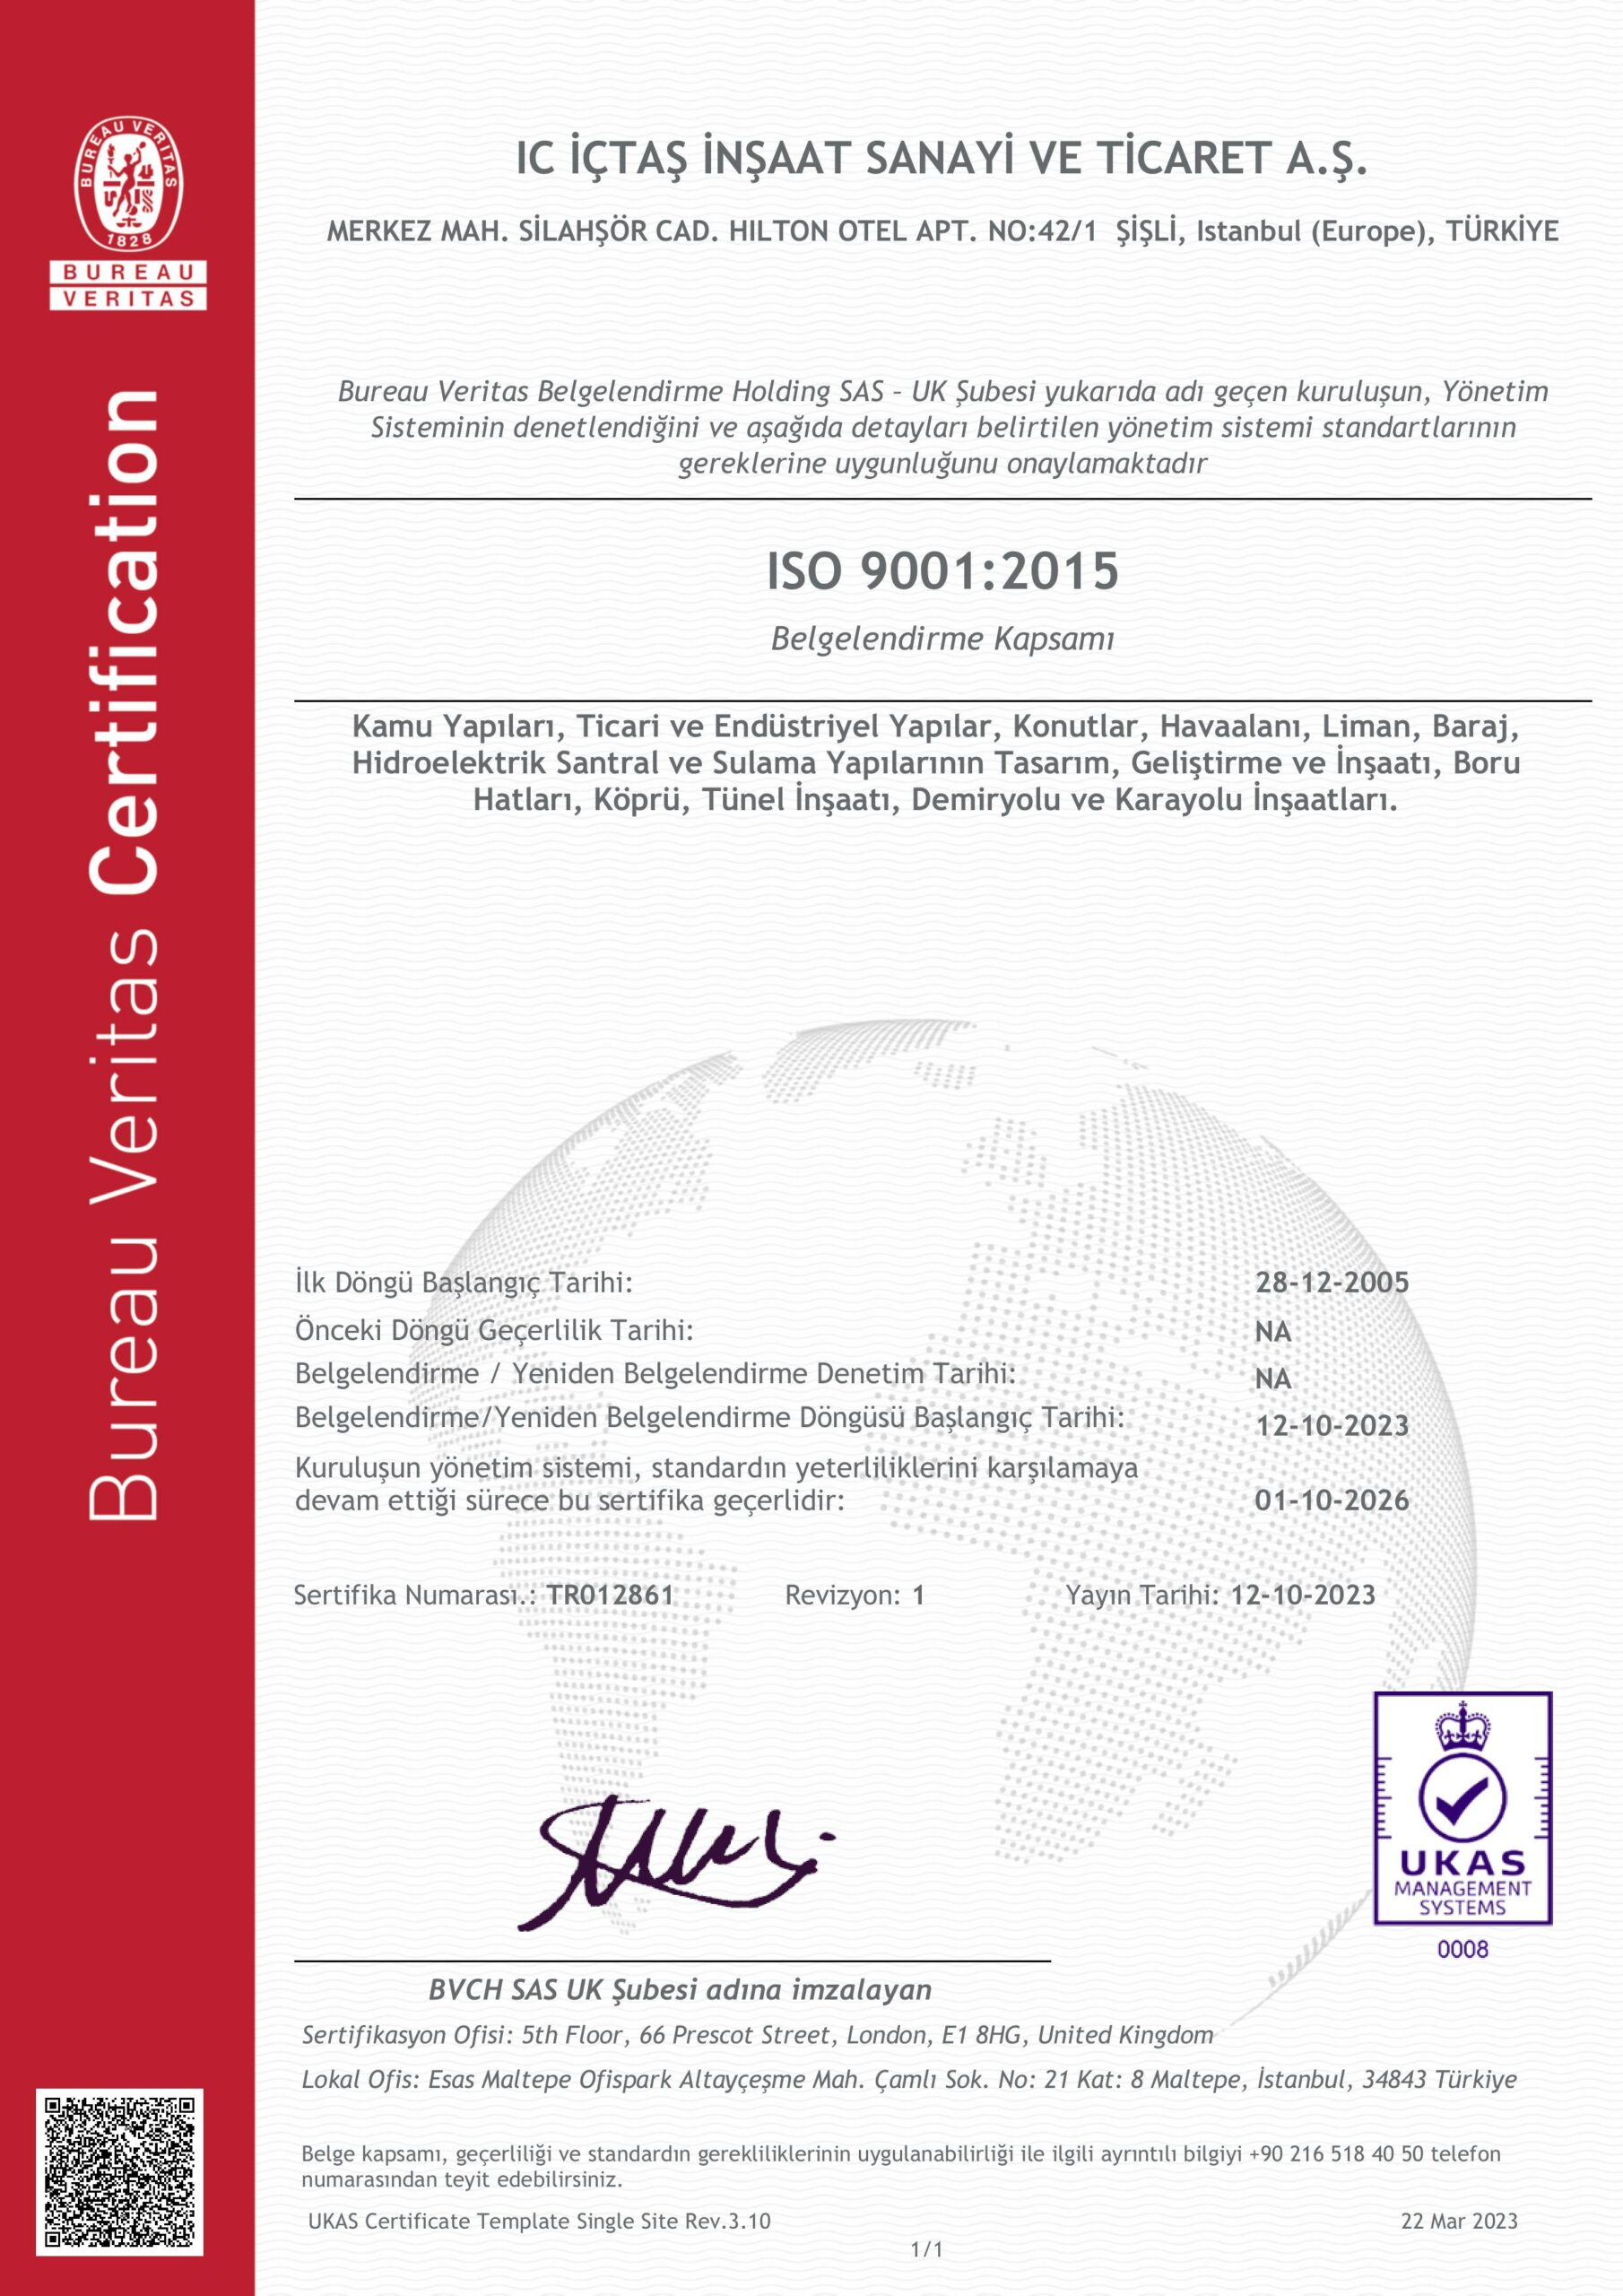
IC İnşaat | ISO 9001 Certification
ISO 9001 Certification
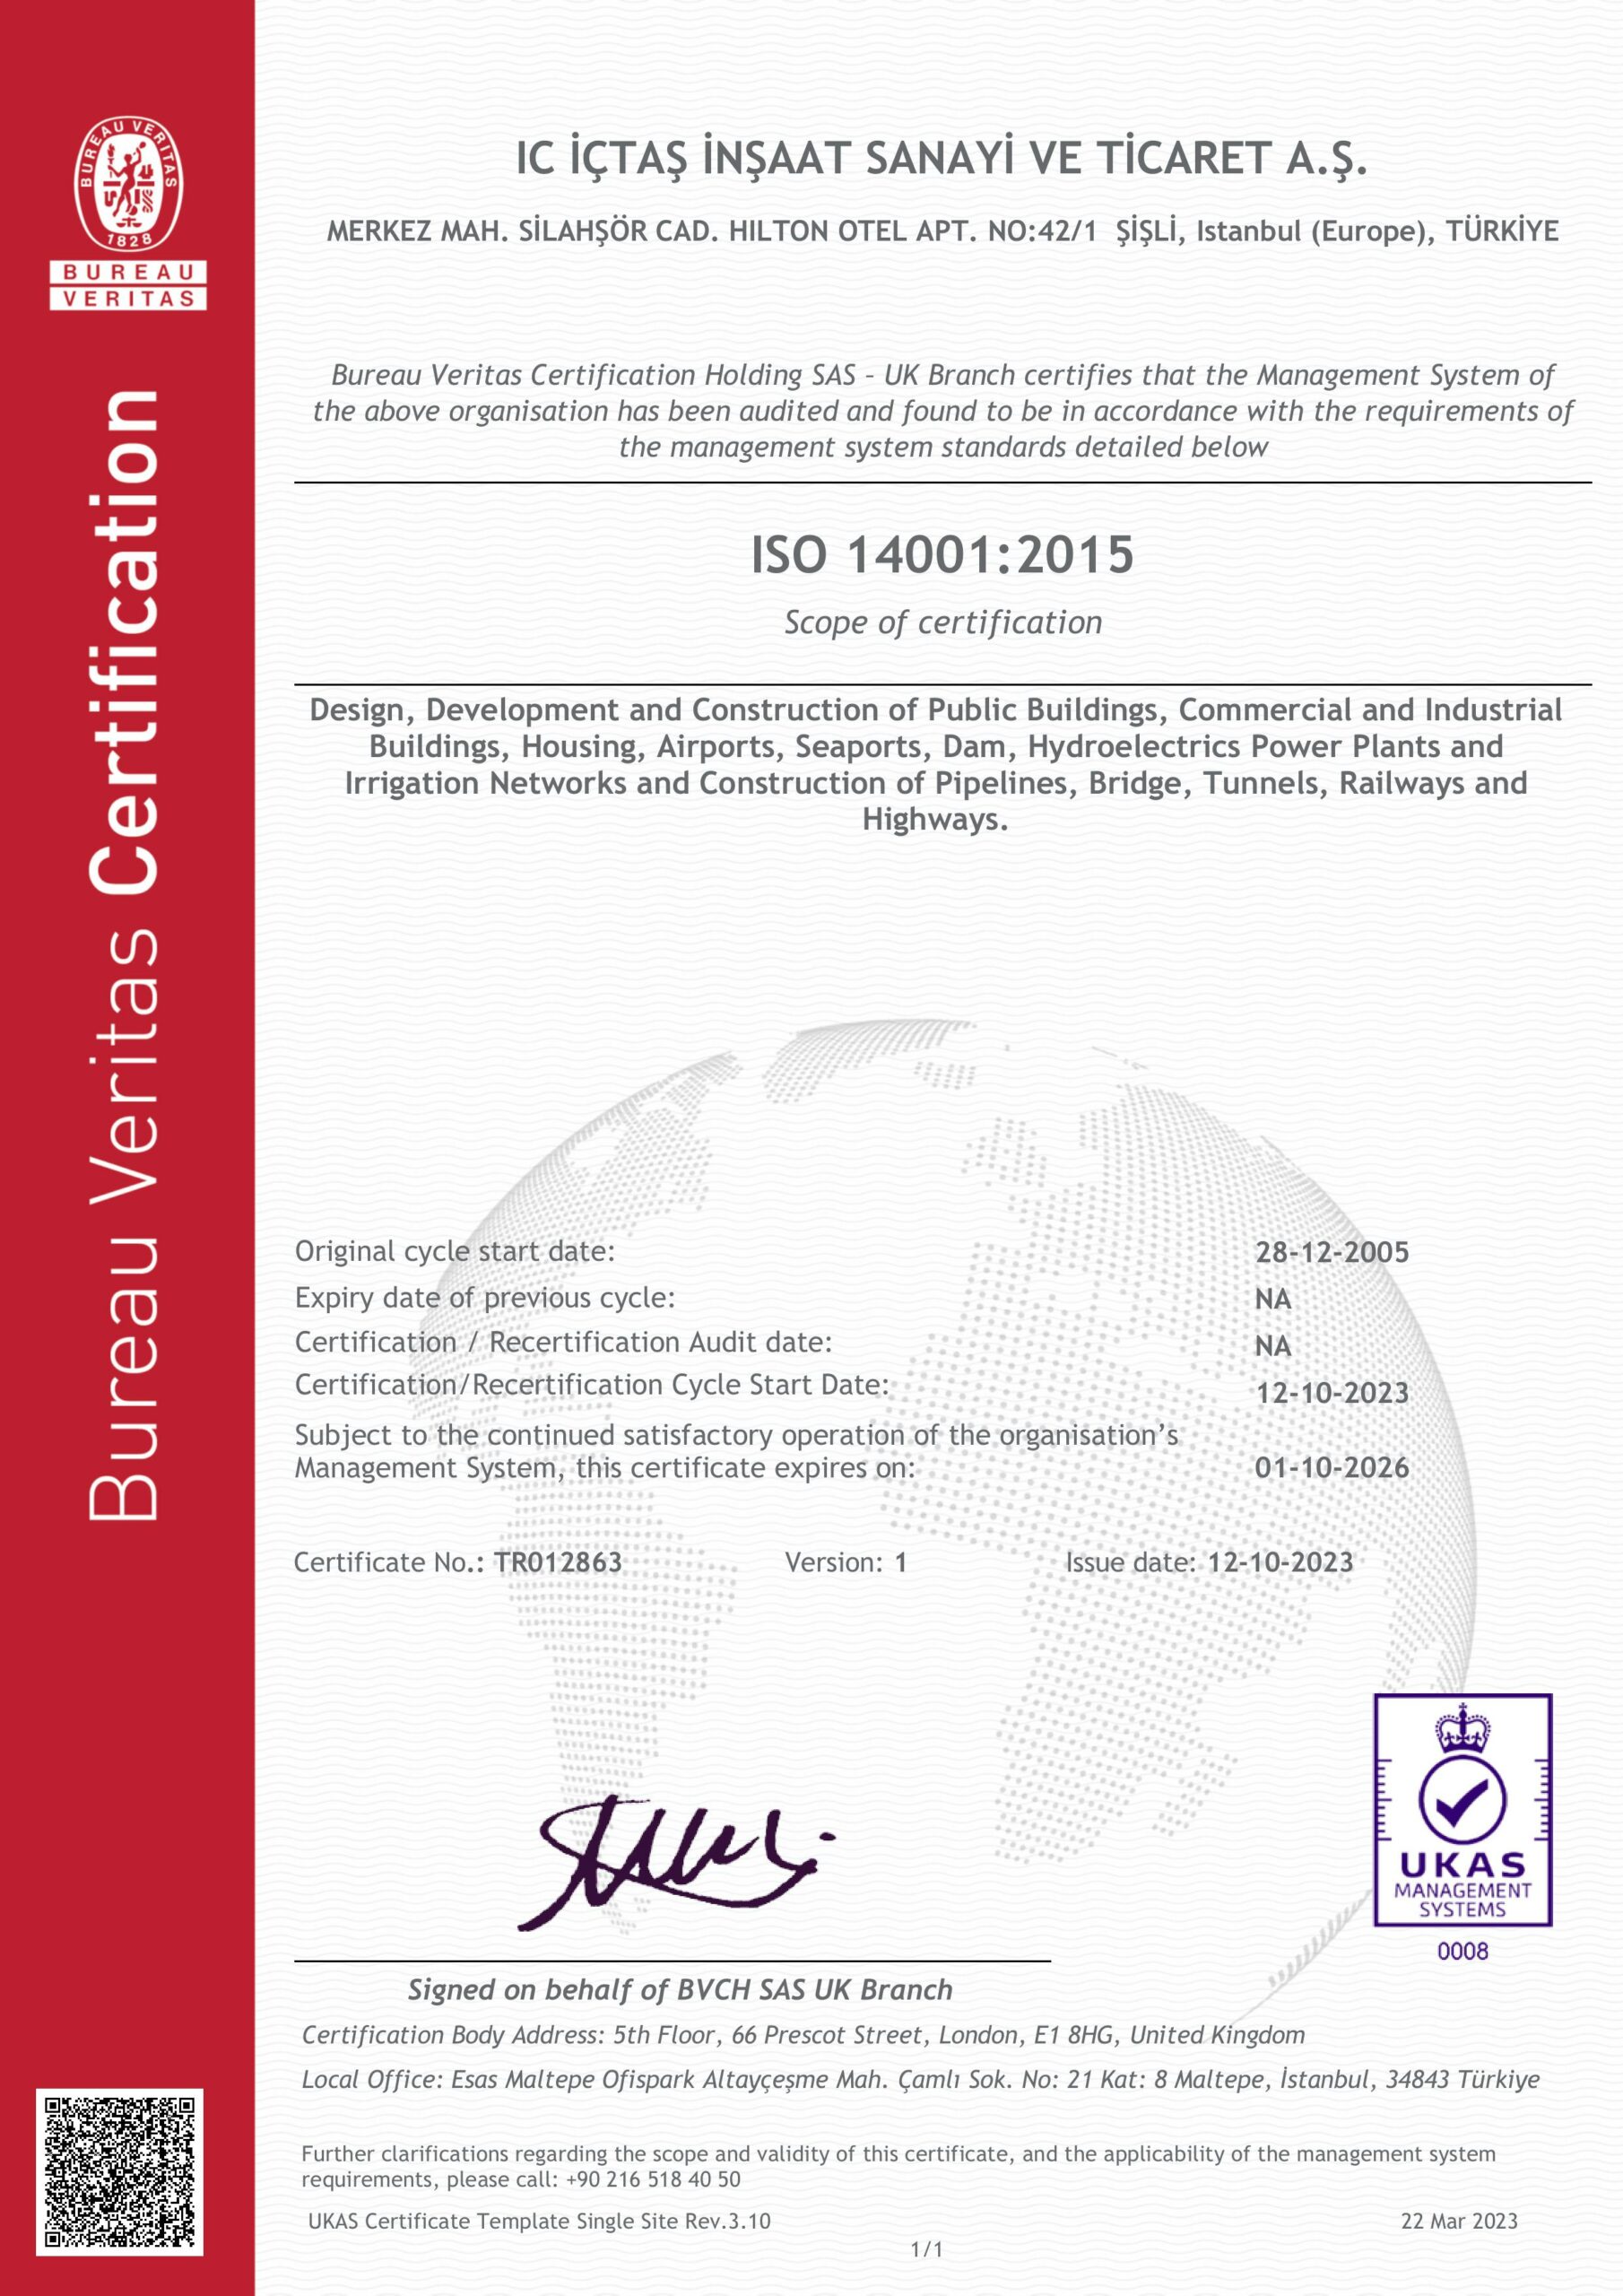
IC İnşaat | ISO 14001 Certification
ISO 14001 Certification
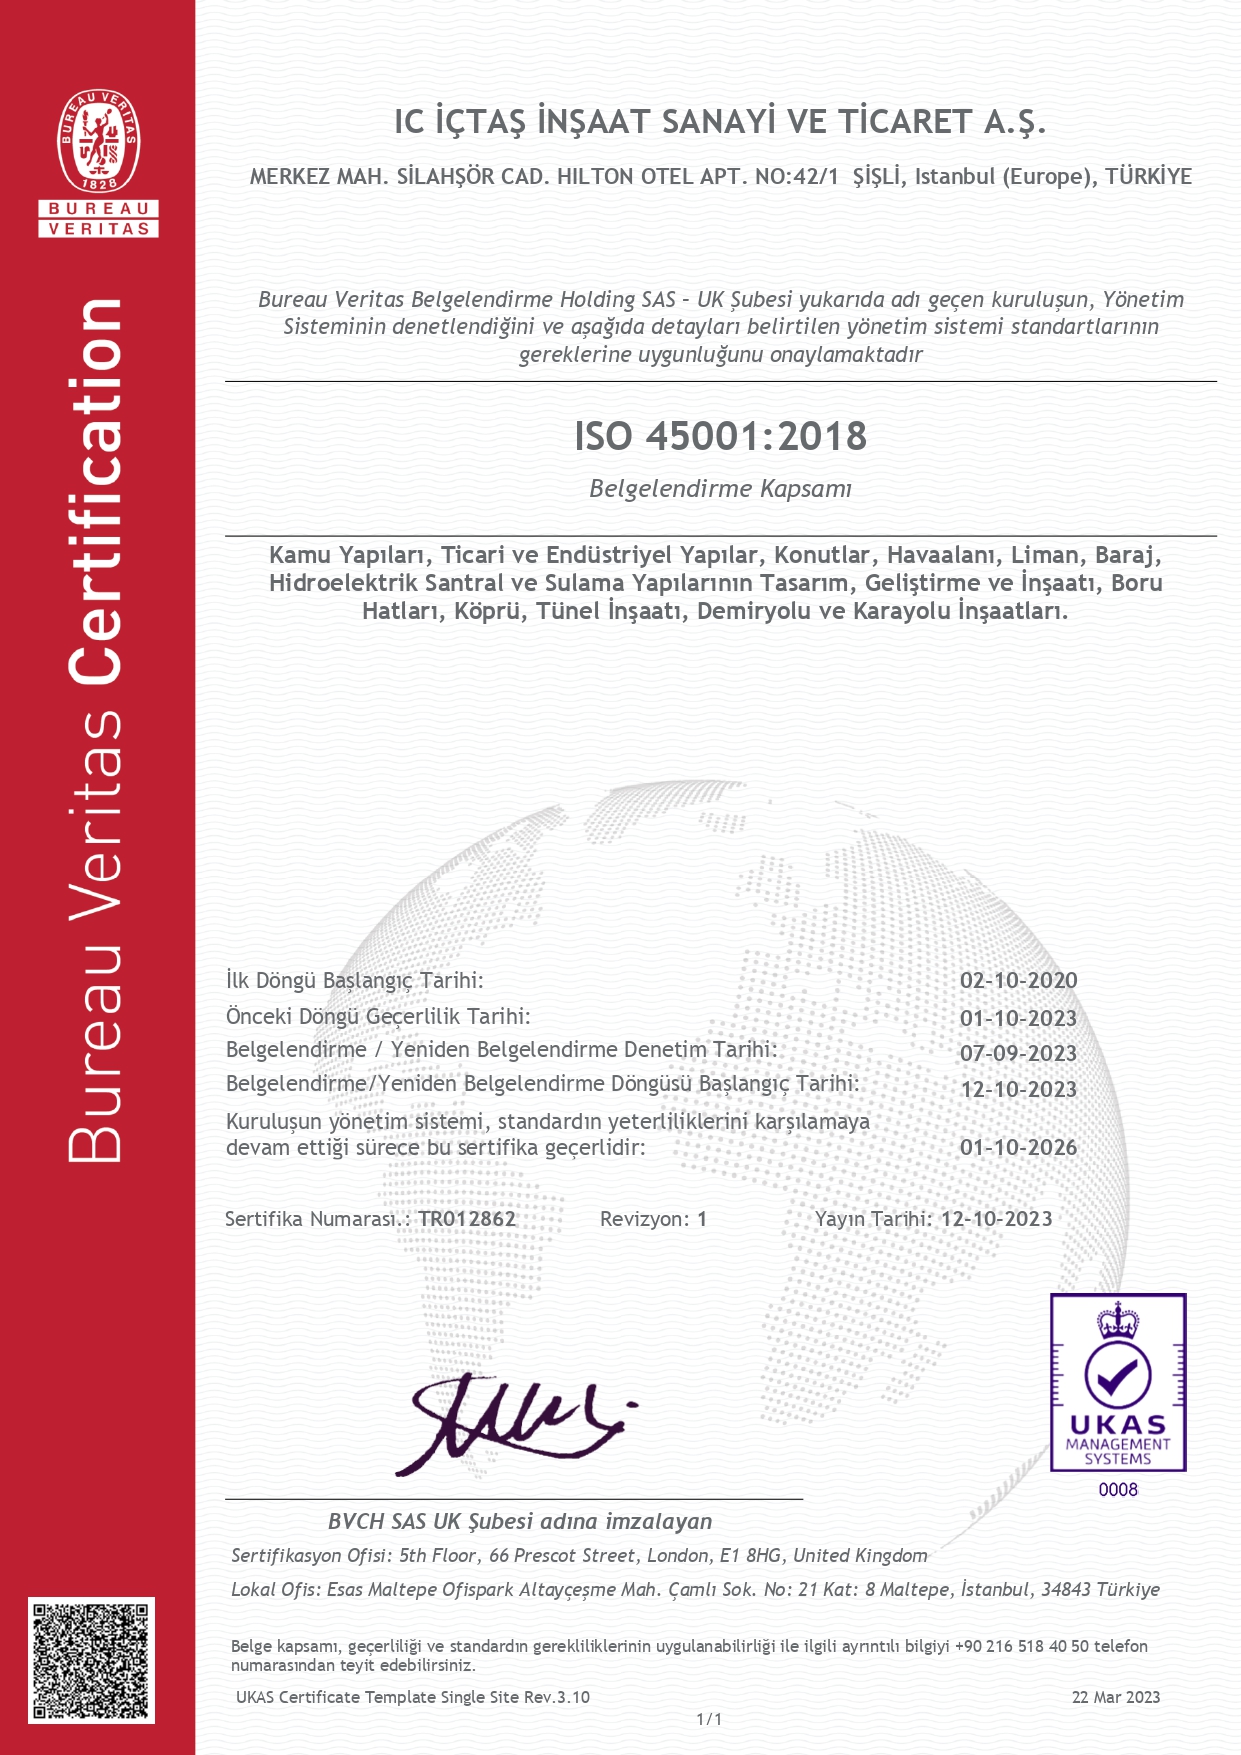
IC İnşaat | ISO 45001 Certification
ISO 45001 Certification
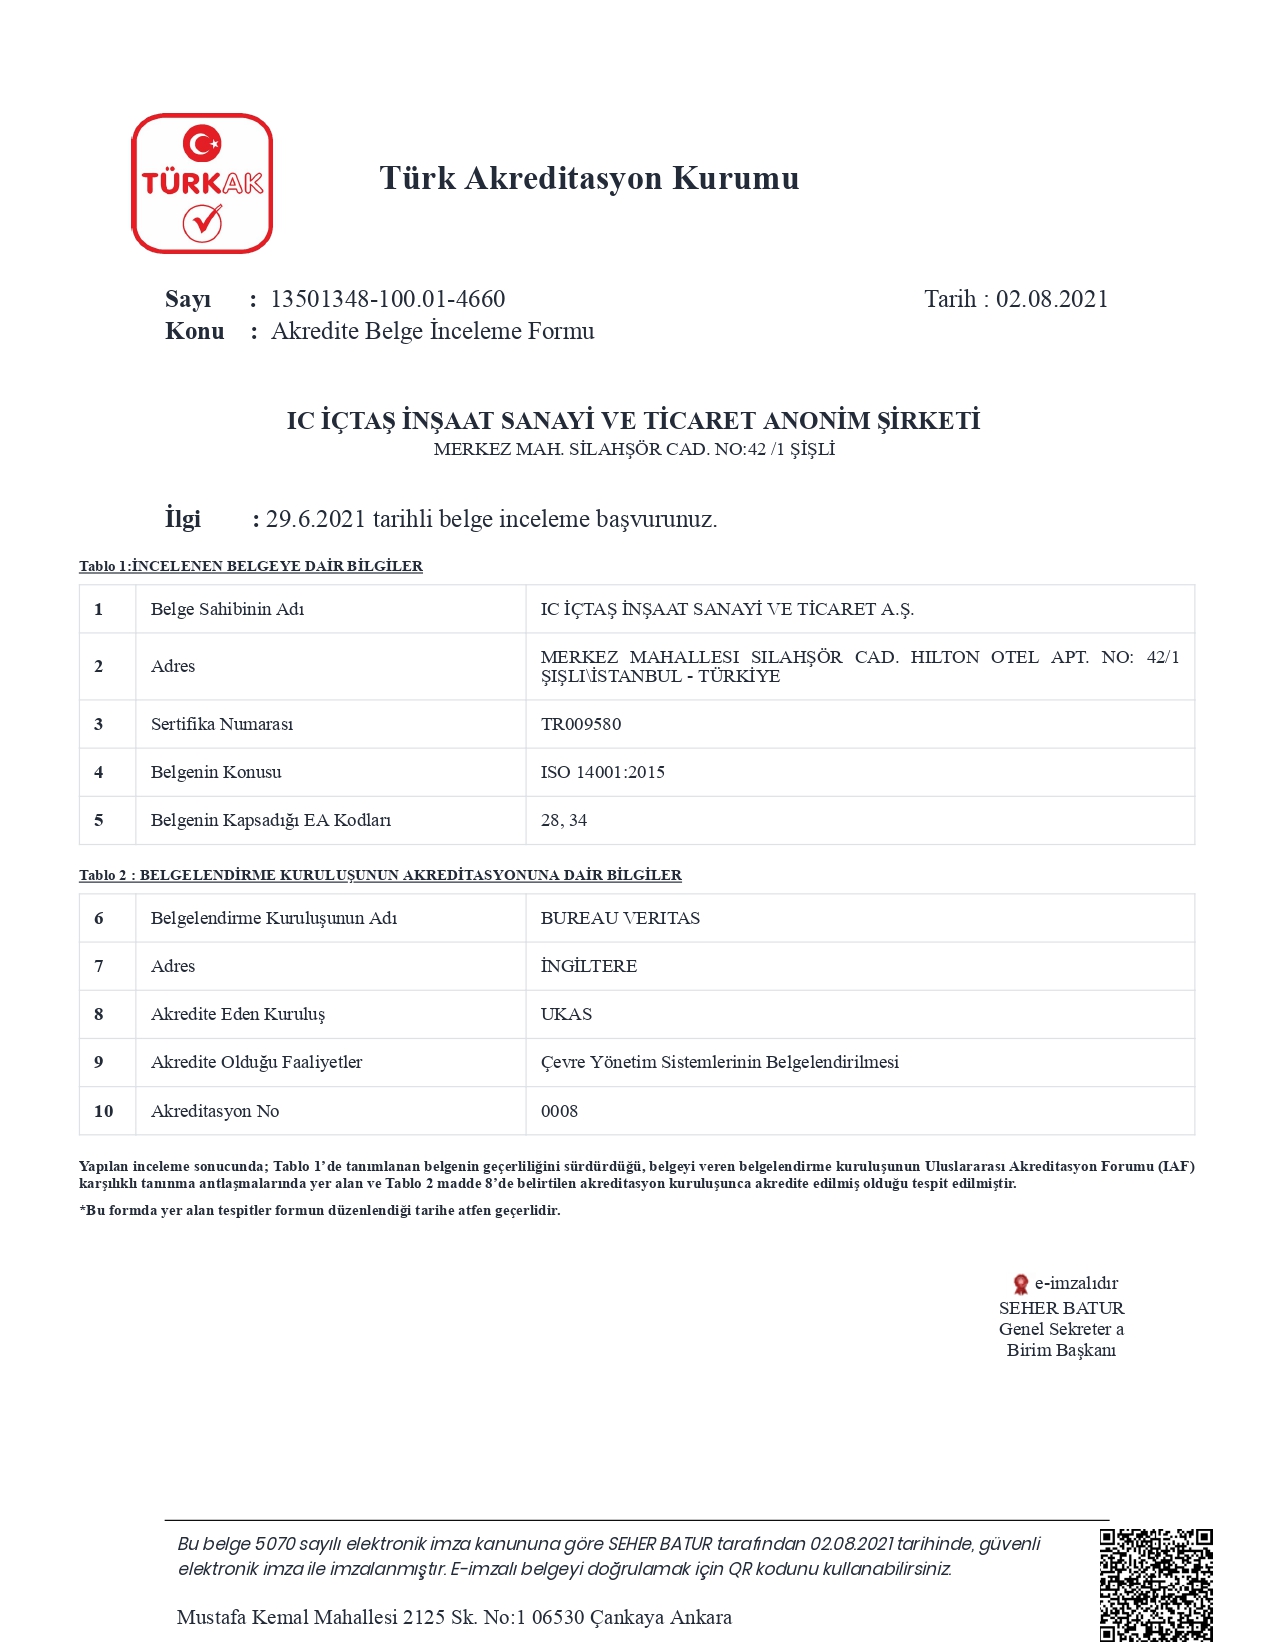
IC İnşaat | TÜRKAK ISO 14001 Certification
TÜRKAK ISO 14001 Certification
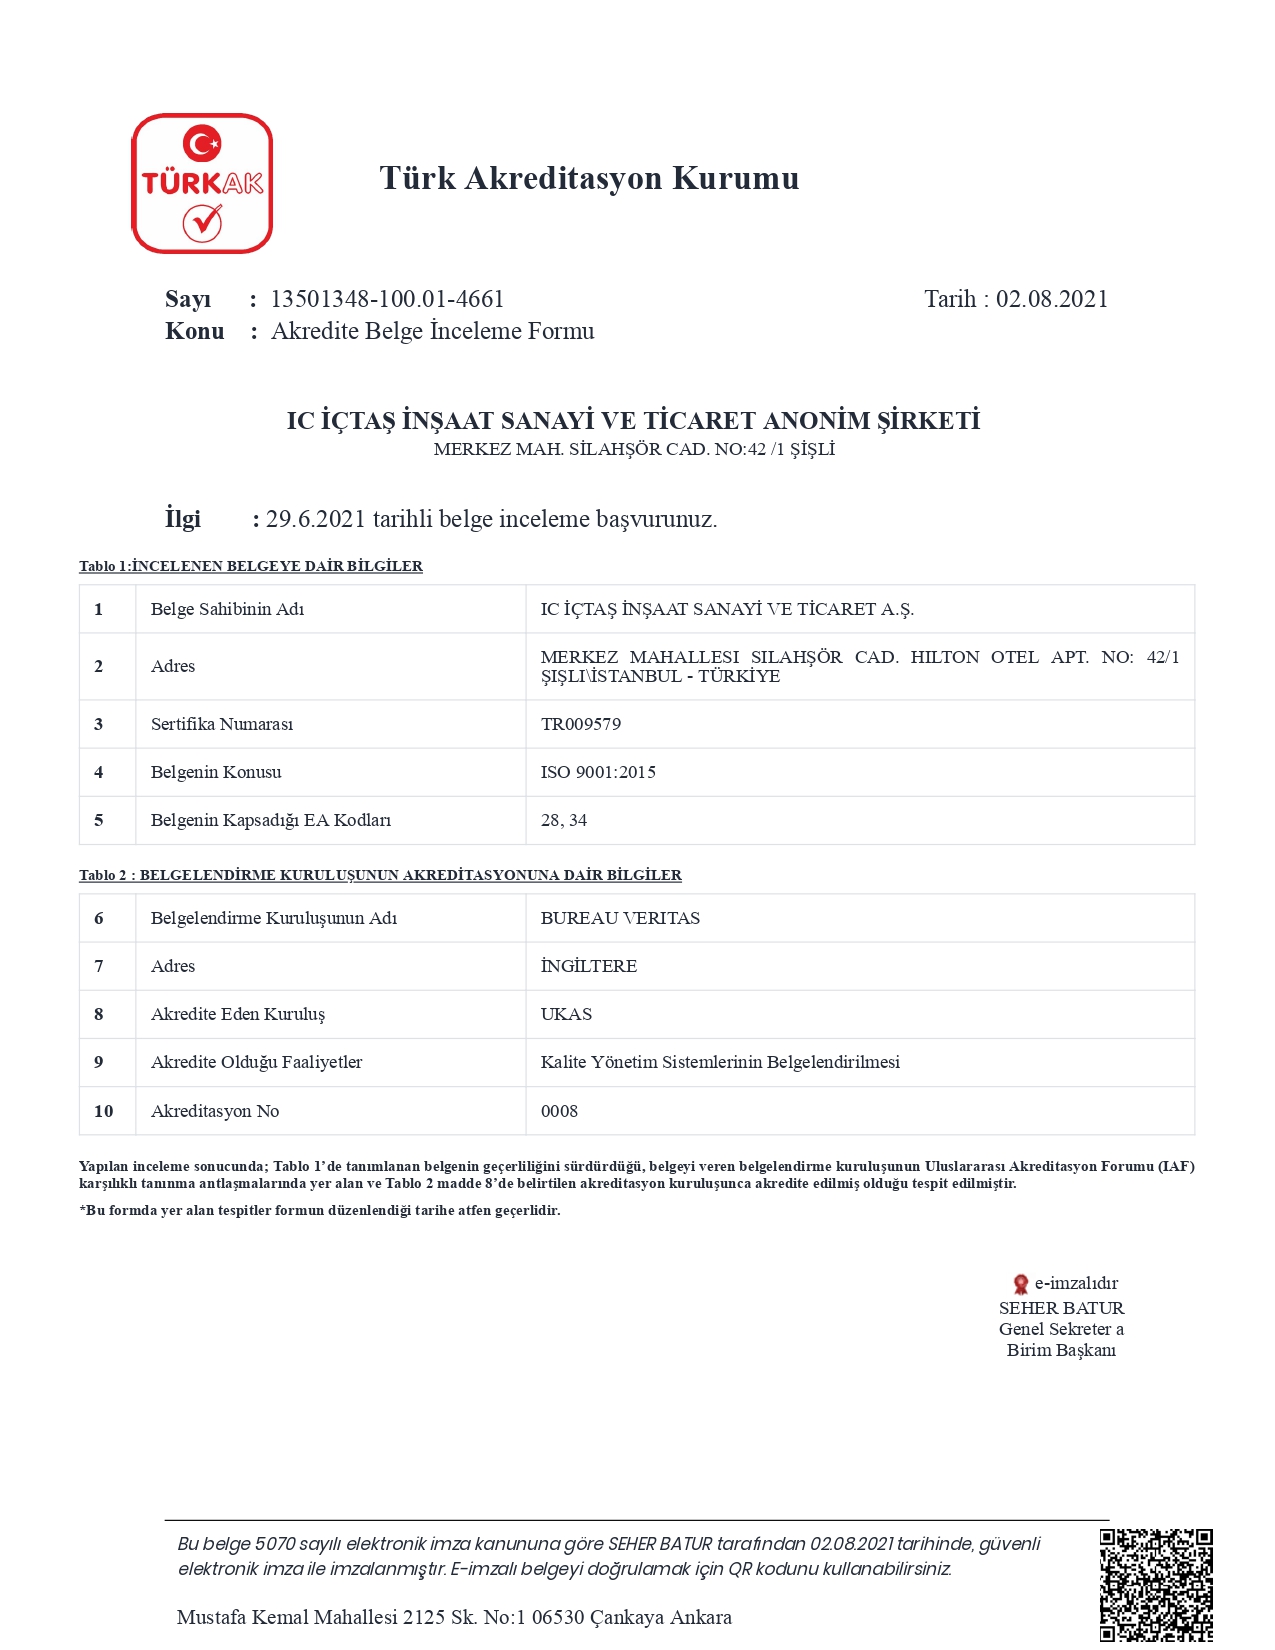
IC İnşaat | TÜRKAK ISO 9001 Certification
TÜRKAK ISO 9001 Certification